Post-Quantum Cryptography in 2026: NIST Standards and Digital System Migration Challenges
A research-based guide to post-quantum cryptography, NIST standards, quantum computing threats, harvest-now-decrypt-later risks, and digital security migration readiness.
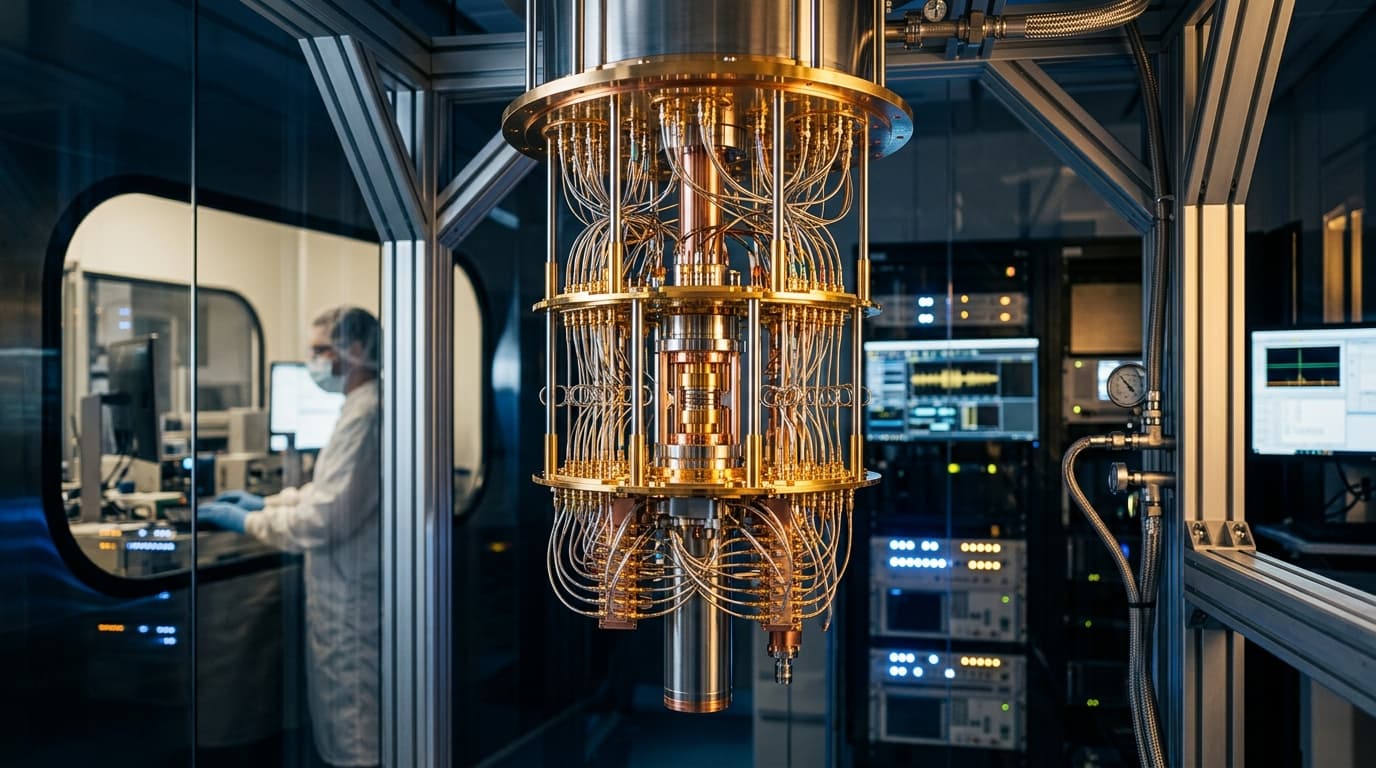
Post-Quantum Cryptography mitigates quantum threats to legacy public-key cryptosystems like RSA and ECC. NIST has standardized ML-KEM, ML-DSA, and SLH-DSA, while HQC and FALCON undergo continued standardization. Successful migration from traditional algorithms to quantum-resistant primitives requires comprehensive cryptographic asset inventory, risk prioritization, vendor support review, and the implementation of architectural crypto agility using AES symmetric layers.
Quantum computers do not yet need to be capable of breaking current encryption for organizations to begin preparing for post-quantum security. The longevity of data confidentiality, potential threats to public key cryptography, and the lengthy process of digital infrastructure updates are already strong reasons to formulate a migration plan early.
This preparation is known as Post-Quantum Cryptography (PQC), which is the use of new mathematical cryptographic algorithms designed to withstand attacks from cryptographically relevant quantum computers (Cryptographically Relevant Quantum Computer / CRQC).
The development of PQC has officially entered the technical implementation stage. The United States National Institute of Standards and Technology (NIST) published three main standards on August 13, 2024. These standards provide a tested foundation that organizations can use to start planning, testing, and applying migration to modern digital infrastructure.
However, there is an important distinction between algorithms that have reached final standard status, algorithms newly chosen for standardization, and candidates still under evaluation. Understanding these differences helps system administrators make decisions based on actual technical status rather than merely following short-lived security trends.
This research article delves into NIST PQC standards, the threat of harvest now, decrypt later, digital system migration challenges, and practical frameworks for organizations to strengthen cyber resilience.
Why Post-Quantum Cryptography Is Critical
Asymmetric cryptography is used in various vital digital security processes, including session key exchange, identity authentication, TLS/SSL digital certificate issuance, and software signatures.
A number of public key algorithms dominating modern digital systems rely on mathematical problems such as the factorization of large prime numbers (RSA) and discrete logarithms on elliptic curves (ECC). A quantum algorithm known as Shor's algorithm can theoretically solve these problems efficiently if run on a quantum computer with a sufficient scale of logical qubits.
This condition does not mean that all modern encryption can already be broken by existing quantum computers today. The operational capability to break modern cryptography on a broad scale requires quantum hardware with highly challenging scale and fault tolerance. The timeframe for achieving this operational capability remains uncertain.
-PQC focuses on algorithms designed to maintain long-term security against such threats, while also running efficiently on conventional computing devices (cloud servers, laptops, IoT microcontrollers, and smartphones).
For system architects at InspirasiKita Technology Research Category, the challenge is not just choosing new algorithms. Cryptography is scattered across applications, operating systems, physical network devices, the Internet Infrastructure & Cloud Hosting layer, digital certificates, identity management systems, and third-party products. Every change plan must thoroughly account for this entire dependency chain.
Official Reference: Global standardization programs can be monitored directly through the official NIST: Post-Quantum Cryptography portal.
The Real Risk: Harvest Now, Decrypt Later (HNDL) Scenario
One of the fundamental reasons why organizations must prepare immediately is the Harvest Now, Decrypt Later (HNDL) scenario.
In this scenario, threat actors intercept and store encrypted data communications today with the expectation of decrypting them in the future when adequate quantum computer technology becomes available. This risk is highly relevant for information that must be kept confidential for many years.
Examples of digital assets vulnerable to the HNDL threat include:
- Trade secrets, innovation blueprints, and corporate intellectual property.
- Medical privacy data, electronic health records, and genomic data.
- Strategic communications and public information sovereignty data.
- Long-term banking transaction records and biometric identity data.
-HNDL is not proof that attackers can currently read all your encrypted communications. The term describes an adversarial hoarding strategy for potential future decryption.
Therefore, organizations should assess digital security risks based on the following five guiding questions:
- Confidentiality Retention Period: How long must the data remain confidential?
- Protection Algorithm Strength: What algorithms and protocols protect data in-transit and at-rest?
- Interception Exposure: Does data traffic traverse public networks vulnerable to third-party interception?
- Transition Time: How long will it take the organization to update all related cryptographic libraries?
- Ecosystem Support: Do the software, operating systems, and vendor services used have a clear upgrade path?
Answers to these questions help determine which system components must be prioritized first.
Three NIST PQC Standards Reaching Final Status (August 2024)
On August 13, 2024, the National Institute of Standards and Technology (NIST) officially approved the first three Federal Information Processing Standards (FIPS) for PQC. All three have specific functions: one standard focuses on shared key establishment, while the other two focus on digital signatures.
All parameter figures and byte size specifications in the following table are official authentic data from NIST FIPS publication documents:
| FIPS Standard | Algorithm Name | Algorithm Origin | Cryptographic Function | Mathematical Approach | Official Parameters & Security Level | Public Key Size | Ciphertext / Signature Size |
|---|---|---|---|---|---|---|---|
| FIPS 203 | ML-KEM | CRYSTALS-Kyber | Key Encapsulation | Module-Lattice | ML-KEM-512 (NIST Cat 1 / ~AES-128) ML-KEM-768 (NIST Cat 3 / ~AES-192) ML-KEM-1024 (NIST Cat 5 / ~AES-256) |
800 Bytes 1,184 Bytes 1,568 Bytes |
768 Bytes 1,088 Bytes 1,568 Bytes |
| FIPS 204 | ML-DSA | CRYSTALS-Dilithium | Primary Digital Signature | Module-Lattice | ML-DSA-44 (NIST Cat 2) ML-DSA-65 (NIST Cat 3) ML-DSA-87 (NIST Cat 5) |
1,312 Bytes 1,952 Bytes 2,592 Bytes |
2,420 Bytes 3,309 Bytes 4,627 Bytes |
| FIPS 205 | SLH-DSA | SPHINCS+ | Hash-Based Digital Signature | Stateless Hash-Based | SLH-DSA-128 (NIST Cat 1) SLH-DSA-192 (NIST Cat 3) SLH-DSA-256 (NIST Cat 5) |
32 - 64 Bytes | 7.8 KB - 17.0 KB 16.2 KB - 35.6 KB 29.7 KB - 49.8 KB |
1. ML-KEM: FIPS 203
Module-Lattice-Based Key-Encapsulation Mechanism (ML-KEM) is used to establish a shared secret between two parties through an open public communication channel. This shared secret is subsequently used by high-strength symmetric algorithms (such as AES-256) to encrypt communication data streams.
ML-KEM originates from the CRYSTALS-Kyber algorithm. FIPS 203 establishes three parameter sets:
- ML-KEM-512: NIST security category 1 (equivalent to AES-128 brute-force computing strength).
- ML-KEM-768: NIST security category 3 (equivalent to AES-192 strength). This is the most recommended parameter for general implementation.
- ML-KEM-1024: NIST security category 5 (equivalent to AES-256 strength).
This security category is part of NIST's rigorous evaluation framework. The category is not a guarantee that software implementations are automatically immune to side-channel attacks, but rather a benchmark of mathematical resilience. Parameter selection must consider security needs, transmission latency, and device interoperability.
ML-KEM is not a direct bulk data encryption algorithm replacing all cryptographic functions; its role is a secure session key exchange mechanism.
- Specification Documentation: NIST FIPS 203: Module-Lattice-Based Key-Encapsulation Mechanism Standard.
2. ML-DSA: FIPS 204
Module-Lattice-Based Digital Signature Algorithm (ML-DSA) is the digital signature standard derived from CRYSTALS-Dilithium.
Digital signatures serve to ensure data integrity (tamper-proof) and authenticate the validity of the signing party. Their utilization includes signing digital documents, TLS identity certificates, and software code signing.
The main challenge in migrating to ML-DSA is its signature size. ML-DSA signatures are thousands of bytes in size (e.g., 3,309 bytes at level 65), much larger than conventional elliptic curve signatures (such as Ed25519 which is only 64 bytes). This can trigger data packet fragmentation on network protocols with limited MTU.
- Specification Documentation: NIST FIPS 204: Module-Lattice-Based Digital Signature Standard.
3. SLH-DSA: FIPS 205
Stateless Hash-Based Digital Signature Algorithm (SLH-DSA) is a hash-based digital signature standard derived from SPHINCS+.
SLH-DSA utilizes a different mathematical approach from lattices. This difference is invaluable in defense-in-depth cryptographic diversification strategies. If theoretical weaknesses in lattice mathematical problems are discovered in the future, SLH-DSA remains robust because it only relies on the security of standard cryptographic hash functions tested for decades.
Although its key size is very compact (32–64 bytes), its signature size is relatively large (reaching tens of kilobytes), requiring careful consideration before deployment in environments with tight bandwidth constraints.
- Specification Documentation: NIST FIPS 205: Stateless Hash-Based Digital Signature Standard.
Status of Advanced Algorithm Development: HQC and FALCON
The PQC standardization process did not stop after the three FIPS standards above were approved. NIST continues to evaluate additional algorithms to expand options and prevent dependency on a single type of mathematical approach:
HQC: Alternative Key Establishment Candidate
In March 2025, NIST selected Hamming Quasi-Cyclic (HQC) to be standardized as an additional code-based key establishment mechanism.
HQC serves as an alternative if anomalies are found in ML-KEM at a later date. However, the selection of HQC for standardization does not mean its final standard has been issued. NIST projects that the final HQC standard will be completed around 2027. Before final documents are released, organizations are advised to prioritize ML-KEM for production implementation.
- Reference: NIST: HQC Selected for Standardization.
FALCON / FN-DSA: Fast Lattice-Based Digital Signatures
FALCON was selected for advanced standardization processes and is listed in the development of FIPS 206 (FN-DSA). FALCON offers significantly more compact signature sizes compared to ML-DSA, but requires more complex high-precision floating-point computing at the hardware implementation level. The FIPS 206 standard is currently still in the official draft finalization stage.
NIST also continues to evaluate additional digital signature candidates in advanced evaluation rounds to enrich the global cryptographic ecosystem.
- Advanced Standard References: NIST: Selected Algorithms for Post-Quantum Cryptography and NIST: Additional Digital Signature Schemes.
Real Challenges of PQC Migration in Digital Systems
Implementing PQC is not merely replacing a single line of application configuration code. According to the research team's evaluation at InspirasiKita Empirical Research Methodology, PQC migration involves profound system architecture transformations:
1. Cryptographic Discovery
Many enterprise systems do not know precisely where cryptography is used. Legacy algorithms are frequently embedded within third-party dependencies, SDK modules, hardware drivers, or external payment gateways. Periodic inventories must be conducted to map all cryptographic assets.
2. Surge in Key Size and Network Latency
PQC public keys and signatures are thousands of bytes in size. This has the potential to cause TCP packet fragmentation, prolong TLS handshake durations, and increase server computing loads. This network latency impact is acutely felt in distributed infrastructure (as discussed in our research on 2026 Edge Computing vs Centralized Cloud Latency Analysis).
3. Vendor Ecosystem and Hardware Dependencies
Many organizations do not control their entire technology stack independently. Hardware Security Modules (HSMs), smart cards, network routers, and public Certificate Authority (CA) certificates depend on update roadmaps from respective vendors.
4. Interoperability and Hybrid Approaches
During the transition period, modern systems must still be able to communicate with legacy systems. The best solution currently is to apply a hybrid approach (for example, combining X25519 with ML-KEM-768 in TLS 1.3 key negotiations), so that systems meet current compliance standards while remaining immune to future decryption threats.
5. Building Crypto Agility
Crypto agility is the ability of a system architecture to centrally update or swap algorithms, key lengths, and certificates without having to overhaul the application codebase. This modular system design guide is outlined by NIST in Considerations for Achieving Crypto Agility (NIST CSWP 39).
Practical 7-Stage Framework to Begin Migration
Organizations can adopt the following structured roadmap to begin their PQC migration journey:
- Stage 1: Form a Cryptographic Steering Committee: Unite cybersecurity teams, infrastructure architects, software developers, risk management divisions, and data owners.
- Stage 2: Build a Complete Cryptographic Inventory: Map all algorithms, SSL/TLS libraries, public certificates, private keys, and cross-system API connections.
- Stage 3: Evaluate HNDL Risk Exposure: Identify data repositories with confidentiality retention periods exceeding 5 to 10 years.
- Stage 4: Map Requirements to FIPS Standards: Apply ML-KEM (FIPS 203) for session key encapsulation and ML-DSA (FIPS 204) for digital signature verification.
- Stage 5: Run Limited Staging Sandbox Tests: Test hybrid cipher negotiations, packet size impacts on network MTU buffers, and client-server connection stability.
- Stage 6: Launch Phased Rollout: Begin migration from external network perimeters and public API gateways before touching core databases.
- Stage 7: Update Governance and Documentation: Document all protocol changes and monitor the latest technical guidelines from NIST NCCoE Migration to PQC FAQ.
Conclusion
In 2026, Post-Quantum Cryptography has shifted from theoretical research to real implementation action plans. Three final FIPS standards from NIST: ML-KEM (FIPS 203), ML-DSA (FIPS 204), and SLH-DSA (FIPS 205): provide legal and technical certainty for the global industry to begin moving.
The most important step for technology managers is not waiting for commercial quantum computers to arrive, but building architectural readiness as early as possible: auditing current cryptographic usage, protecting long-lived data from harvest-now-decrypt-later threats, and instilling crypto agility principles across every line of digital information systems.
Frequently Asked Questions (FAQ)
Verified technical clarification for readers and search clarity.
Post-Quantum Cryptography secures digital systems against threats from both classical and relevant quantum computers. Its algorithms are designed to run efficiently on standard, conventional computing hardware.
Topics & Related Industries:
More on Technology
Deep dives into system architectures, enterprise workloads, and modern benchmarks.
Edge Computing vs Centralized Cloud Latency Benchmark 2026
Empirical benchmark evaluating P95 and P99 latency between distributed edge nodes and traditional centralized cloud clusters across Asia-Pacific.
Evolution of Digital Entertainment Portals & Modern JKT88 System
Comprehensive analysis of digital entertainment portal evolution in the JKT88 ecosystem, highlighting system architecture and online user experience.
Zero Trust Implementation for the Protection of Digital Public Service Infrastructure
A security architecture study of digital public services based on Zero Trust Architecture, NIST identity management integration, and advanced transport encryption.