AI Agent Security in 2026: Identity Risks, Access Rights, and Automation
Explore AI agent security risks in 2026, ranging from identity and access rights abuse to prompt injection, malicious automation, and human oversight.
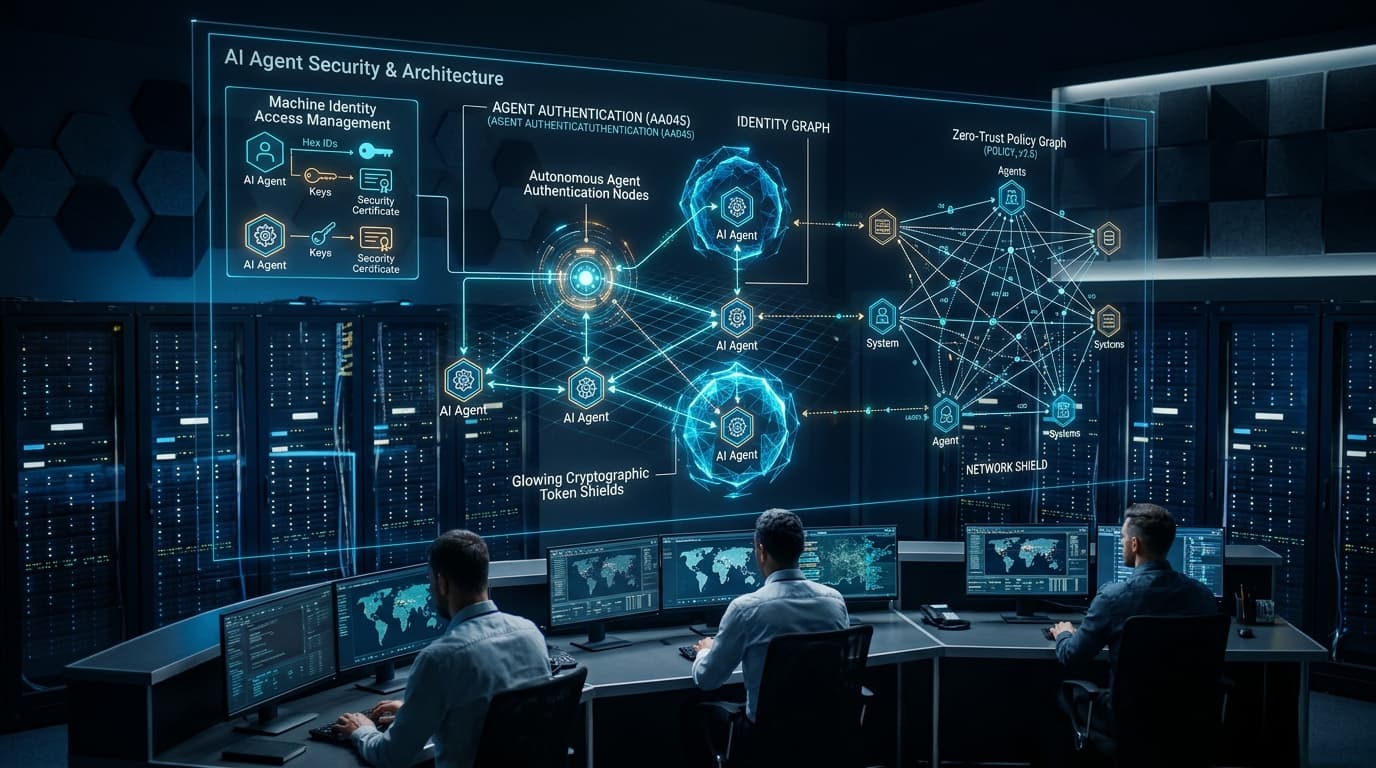
Agentic AI security encompasses machine identity governance, dynamic credential management, and authorization frameworks to mitigate prompt injection and excessive privileges, aligning with Gartner's 2026 cybersecurity trends and NIST guidelines. Organizations must implement granular access controls tailored to specific autonomy levels, distinguishing varying risk profiles across automated digital agents, software tools, and interconnected enterprise services.
AI Agent Security in 2026: Identity, Access Rights, and Automation Risks
AI agents are beginning to be deployed to execute tasks far more complex than simply answering questions. Depending on their design and granted permissions, an agent can utilize tools, retrieve information from other systems, invoke services, modify data, or execute sequences of actions automatically.
These capabilities make AI agents attractive for business and operational needs. However, the ability to act also expands the attack surface. If an agent uses overly broad credentials, accepts malicious instructions from untrusted sources, or executes actions without adequate verification, the impact can far exceed the errors of a typical chatbot.
In the 2026 cybersecurity trends report from Gartner, security oversight for agentic AI and the adjustment of identity and access management for AI agents have become critical concerns. The World Economic Forum via the Global Cybersecurity Outlook 2026 also positions AI-related risks as a vital component of the cybersecurity landscape.
This trajectory indicates that AI agent security must be designed as an integral part of an organization's security architecture, rather than merely as a configuration within the AI model.
What Are AI Agents and Why Do Their Risks Differ?
An AI agent is a system that leverages AI capabilities to assist in achieving goals through one or more steps. Depending on the implementation, an agent can select actions, utilize tools, retrieve context from external sources, and proceed with processes based on the outcomes of previous steps.
The term AI agent encompasses a wide range of systems. Some agents merely generate recommendations, others can read data, and some are granted permission to modify information or execute actions within other systems. Consequently, their risk levels cannot be assessed based solely on the "AI agent" label.
The critical distinction lies in their ability to act and the scope of their authority.
A chatbot that only provides answers may primarily pose risks related to misinformation, data leakage within conversations, or inappropriate responses. Agents connected to business systems may carry additional risks because their outputs can be translated into real-world actions.
For example, an agent that only summarizes reports has a different risk profile than an agent capable of sending emails, updating databases, creating tickets, accessing internal documents, or initiating transactions. Risk depends on the access granted, the actions permitted, and the quality of oversight and security mechanisms in place.
Thus, the relevant security questions are not just "Is this model safe?" but also:
- What identity does the agent use?
- What data and systems can it access?
- What actions is it authorized to perform?
- How are instructions and action outcomes verified?
- Who is responsible if the agent's actions lead to unintended consequences?
These questions form the foundation for building security controls that are commensurate with an agent's capabilities.
Key AI Agent Security Risks in 2026
1. Ambiguous Agent Digital Identity
When an agent interacts with applications, APIs, databases, or internal services, the system must identify who or what is making the request. If agent activity relies on shared accounts or user credentials without adequate separation, organizations may struggle to distinguish human actions from automated ones.
This issue extends beyond activity logging. Ambiguous identities can complicate access control restrictions, incident investigations, permission revocation, and accountability.
For instance, if multiple agents use the same service credential, activity logs might show the account being used without providing a clear picture of which agent initiated the action. If those credentials are compromised, the scope of the impact becomes significantly harder to determine.
A more secure approach is to provide distinct identities for each agent or agent context as required by the architecture. These identities must be linked to access policies, activity logging, and permission revocation mechanisms.
In February 2026, NIST published a concept paper on the identity and authority of software agents to invite public feedback. Topics covered include identification, authorization, auditing, and action accountability. The paper serves as an exploratory step rather than a final standard that automatically applies to all organizations.
2. Overly Broad Access Rights
AI agents often require access to tools or services to complete tasks. However, granting overly broad permissions increases the potential impact if an agent misinterprets a goal, is manipulated, or executes unauthorized actions.
For example, an agent that only needs to read data to generate a summary should not automatically receive permissions to delete data, modify configurations, or manage accounts. Access rights that exceed requirements can turn limited errors into more serious incidents.
The relevant principle is least privilege, which involves granting the minimum access rights necessary for a specific task. Implementation should cover not only data access but also the ability to execute actions.
Organizations can differentiate permissions for:
- Reading information.
- Creating or updating data.
- Deleting information.
- Sending communications to third parties.
- Accessing sensitive data.
- Modifying configurations or access rights.
- Initiating transactions or high-impact actions.
Such separation helps ensure that agents do not possess authority beyond what is required. Permissions should also be restricted based on tasks, context, duration, and the environment in which the agent operates.
Access rights must be re-evaluated when an agent's functions change. An agent that initially only read documents might gain additional capabilities after new integrations are installed. Without periodic reviews, legacy permissions can become overly broad for the agent's actual tasks.
3. Prompt Injection and Goal Manipulation
AI agents can process information from documents, web pages, emails, search results, or other external sources. Such information is not always trustworthy. Malicious content may attempt to influence the agent to ignore instructions it should follow or to perform actions outside its original purpose.
One relevant risk is prompt injection. In this attack, malicious instructions are inserted into the input or content processed by the AI system. For agents with access to tools, such manipulation becomes even riskier if the agent acts upon untrusted content without adequate verification.
As an illustration, an agent might be asked to summarize a document. That document could contain instructions attempting to trick the agent into revealing other information or sending data to a specific destination. Such content should be treated as data to be analyzed, rather than automatically as authoritative instructions capable of altering the agent's task.
Separating trusted instructions from the content being processed is a critical part of mitigation. However, robust system instructions alone are insufficient to guarantee security. Controls must also be applied to available tools, access permissions, action validation, and data delivery paths.
Steps that can be considered include:
- Treating external content as untrusted input.
- Limiting the tools an agent can invoke.
- Verifying parameters and action goals before execution.
- Preventing the transmission of sensitive data to unauthorized destinations.
- Testing agents with relevant prompt injection scenarios.
- Logging actions taken after processing external sources.
NIST discusses the evaluation of agent hijacking and prompt injection risks in its technical article on strengthening AI agent hijacking evaluations. Meanwhile, the OWASP Top 10 for Agentic Applications 2026 covers risk categories such as agent goal manipulation, tool misuse, and identity and privilege abuse.
4. Tool Misuse and Integration
The ability of an agent to use tools is a source of both benefits and risks. These tools can include APIs, internal functions, browsers, ticketing systems, email services, document storage, or business applications.
Risks arise when an agent can invoke tools without appropriate restrictions, use incorrect parameters, or execute actions that are not actually necessary to complete a task.
For example, a customer support agent might require access to read order statuses. If the integration also grants access to modify customer data or process refunds without additional checks, agent errors or manipulation could lead to significant consequences.
Therefore, security must be implemented at the integration layer, not just at the model level. Each tool should have clear functions and permissions. Parameters must be validated, access to data restricted, and sensitive actions must undergo appropriate verification.
Organizations also need to review third-party dependencies. Components, libraries, plugins, connectors, and services used by the agent can introduce their own risks if not managed properly.
The practical principle is: do not give an agent a tool simply because it is available. Provide only the capabilities truly required by the task and ensure that the actions the tool can perform are fully understood.
5. Error Automation and Cascading Impacts
Automated systems can execute actions rapidly and repeat the same patterns across numerous objects or processes. While beneficial for routine tasks, this capability can also amplify the impact of errors.
If an agent makes an incorrect decision and subsequent processes accept that result without verification, the error can propagate to other steps. Risk increases when multiple agents or services are interdependent, especially if one output serves as the basis for the next automated action.
For example, an agent that miscategorizes a ticket might route it to the wrong workflow. If the subsequent system automatically changes the status, sends notifications, or updates records based on that result, a single initial error can trigger a series of changes.
This example illustrates a possibility, not a claim that all agentic systems experience the same failure patterns. The actual impact depends on workflow design, permissions, validation, and recovery mechanisms.
Several controls can help limit the impact:
- Set limits on the number or type of actions that can be performed within a given period.
- Use validation before critical changes are applied.
- Implement transaction limits or scope limits for changes.
- Provide termination and recovery mechanisms.
- Monitor activity patterns that deviate from expected behavior.
- Separate high-risk actions from automated processes that do not require approval.
The goal is not to eliminate automation, but to ensure that the speed of agents does not remove the opportunity to detect and stop errors.
6. Weak Activity Logging and Accountability
If agents perform actions across various tools and services, organizations require sufficient records to understand what transpired. Without adequate logs, investigations may struggle to determine whether an action originated from a user, an agent, an integration, or another automated process.
Useful logging should include the agent identity, requester identity, task executed, tools invoked, time of action, impacted objects, execution results, and approvals granted if required.
Logging must also account for privacy and security. Overly comprehensive logs may store unnecessary sensitive information. Organizations need to determine what data is logged, who can access it, how long the data is retained, and how log integrity is protected.
For high-risk actions, records must help link the initial request, decisions, approvals, and final outcomes. This provides organizations with a stronger foundation for audits, investigations, and control improvements.
Securing AI Agents: Priority Controls
No single control can eliminate all AI agent risks. A more robust approach combines identity, access rights, action validation, oversight, and incident response.
1. Implement Auditable Agent Identities
Every agent or execution context must be distinguishable according to system requirements. Avoid using shared credentials that make actions difficult to trace.
Identities must be linked to authorization policies and activity logging. If an agent is disabled or suspected of misuse, organizations need a way to revoke its access without disrupting unrelated identities or services.
2. Utilize Least Privilege and Contextual Restrictions
Grant the minimum access necessary. Separate read and write permissions, limit the scope of information sources, and avoid permanent access if temporary permissions can fulfill the requirement.
Whenever possible, permissions should be granted for specific tasks and revoked once the task is complete. This approach helps reduce risks from long-lived credentials or agents acquiring capabilities beyond their initial requirements.
3. Require Approval for High-Risk Actions
Not all actions require human approval. Repetitive, low-impact tasks can be automated if controls are adequate. However, actions such as deleting critical data, modifying access rights, sending sensitive information to external parties, or initiating high-value transactions may require additional approval.
Approval criteria should be determined based on impact and context, rather than solely on the type of AI model being used.
Approvals must also be meaningful. Reviewers need to understand the action to be taken, the objects affected, and the relevant consequences. Approval buttons without sufficient context do not provide effective oversight.
4. Validate Every Action at the Execution Layer
Do not rely solely on the agent to follow instructions. The system executing the action must verify whether the request is permitted.
For example, before an API modifies data, the system can check the caller's identity, permission scope, parameter format, target objects, and applicable business policies. In this way, controls remain effective even if the agent produces an incorrect decision.
Validation at the execution layer is critical because AI models can produce inconsistent outputs or misunderstand context.
5. Implement Monitoring and Impact Limits
Monitor agent actions, not just the quality of their responses. Activities to watch include spikes in tool calls, access to unusual data sources, attempted unauthorized actions, repetitive changes, or usage of access rights outside of normal patterns.
Also, define impact limits, such as caps on the number of changes, allowlists for destinations, or mandatory check requirements for specific actions. Provide mechanisms to stop agents and revoke access when suspicious activity is detected.
Monitoring must be accompanied by clear incident response procedures. Teams must know who is authorized to stop an agent, how to secure evidence, and how to recover the system after an incident.
6. Test Agents Before and After Deployment
Testing should cover more than just whether the agent can complete its intended tasks. Organizations need to examine how agents handle conflicting instructions, malicious inputs, incomplete data, tool failures, and access rights boundaries.
Testing must also be repeated whenever models, prompts, tools, connectors, policies, or workflows change. Changes to one component can affect the overall system behavior.
Test results should be documented, including scenarios, conditions, outcomes, limitations, and corrective actions. Do not conclude that an agent is entirely secure simply because it passed a number of test scenarios.
What Does the 2026 Security Report Emphasize?
A number of publications in 2026 provide context for organizations beginning to implement agents.
Gartner highlights the need for security oversight of agentic AI and the adjustment of identity and access management for AI agents. The practical implication is that organizations need to know which agents are being used, distinguish between approved and unmanaged usage, and prepare appropriate controls and incident response procedures. Read the Gartner report on 2026 cybersecurity trends.
The World Economic Forum, through the Global Cybersecurity Outlook 2026, reports that 94% of its survey respondents expect AI to be the most significant driver of cybersecurity change. The report also notes that the proportion of organizations assessing the security of AI tools before deployment increased from 37% in 2025 to 64% in 2026.
These figures are the result of surveys and represent the views or practices of respondents. They should not be interpreted as global AI security incident rates or as evidence that every organization has implemented effective controls.
WEF also discusses AI-related vulnerabilities as a growing concern. For organizations, this reinforces the rationale for incorporating AI security evaluations into procurement, development, and system deployment processes.
NIST published a concept paper exploring the identity and authority of software agents in February 2026. This publication indicates ongoing work to adapt identity and authorization concepts to systems capable of acting autonomously. However, this concept paper should not be cited as a final standard.
OWASP provides the Top 10 for Agentic Applications 2026, which addresses risk categories in agentic applications, including goal manipulation, tool misuse, identity or privilege abuse, and supply chain risks. The list is useful as a framework for identifying areas that need testing, but it does not replace risk assessments specific to an organization's systems.
AI Agent Security Checklist for Organizations
Before deploying AI agents into critical workflows, organizations can use the following checklist as a starting point.
- Inventory all agents in use, including those built by internal teams and those provided by vendors.
- Document the owner, purpose, model, tools, connectors, and systems accessible to each agent.
- Establish traceable identities and avoid shared credentials without adequate controls.
- Restrict access rights based on tasks and the principle of least privilege.
- Separate permissions for reading, modifying, deleting, and sending data.
- Define actions that require human approval.
- Validate parameters and authorization at the execution layer.
- Test for prompt injection, tool misuse, and attempts to exceed access privileges.
- Enable sufficient logs for auditing without storing unnecessary sensitive data.
- Define action limits, termination mechanisms, and recovery procedures.
- Review security again after any changes to models, tools, prompts, or workflows.
- Prepare incident response procedures specific to actions performed by agents.
This checklist is not a security certification and does not guarantee that all risks have been eliminated. Use it as a foundation for review, which should then be adjusted according to your architecture, data types, business impact, and organizational obligations.
Conclusion
AI agent security in 2026 is increasingly tied to an organization's ability to control automated actions. Ambiguous identities, overly broad access rights, prompt injection, tool misuse, and weak logging can heighten risks when agents are connected to real-world systems.
A safer approach does not rely solely on models providing correct answers. Organizations need to implement auditable identities, least-privilege access, action validation, approvals for high-risk operations, monitoring, and recovery procedures.
A realistic first step is to map the agents already in use and document what each agent is capable of doing. Afterward, organizations can adjust permissions, test relevant attack scenarios, and ensure that every critical action is traceable.
AI agents can help automate work, but their authority must remain aligned with their purpose and risk profile. The greater an agent's ability to act, the more critical it is to have controls that limit, verify, and log its actions.
💡 Related Research: Post-Quantum Cryptography in 2026: NIST Standards and Digital System Migration Challenges
Frequently Asked Questions (FAQ)
Verified technical clarification for readers and search clarity.
AI agent security encompasses controls designed to protect autonomous agents, underlying data, integrated tools, and connected systems. It spans identity management, access control, input sanitization, action validation, runtime monitoring, and incident response frameworks.
Topics & Related Industries:
More on Apps & Software
Deep dives into system architectures, enterprise workloads, and modern benchmarks.
Cold Start Architecture in Edge Runtimes for Enterprise Applications
Examining cold start architecture in edge runtimes, WebAssembly binary optimization, QUIC network latency mitigation, and enterprise scalability strategies.
Evolution of Digital Entertainment Portals & Modern JKT88 System
Comprehensive analysis of digital entertainment portal evolution in the JKT88 ecosystem, highlighting system architecture and online user experience.
Zero Trust Implementation for the Protection of Digital Public Service Infrastructure
A security architecture study of digital public services based on Zero Trust Architecture, NIST identity management integration, and advanced transport encryption.